The Global Technology Industry Association (GTIA) wants to help shape government regulation of IT service providers by developing standards that public authorities can draw on.
GTIA chief executive Dan Wensley said the association was working to establish professional, operational and technical standards that could help governments determine what should be expected of organisations responsible for managing customers’ IT systems and data.
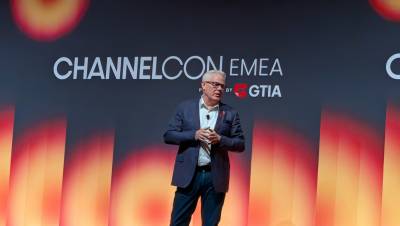
Speaking to Think Digital Partners at GTIA’s ChannelCon EMEA event, Wensley (pictured) argued that governments were increasingly looking at the responsibilities of IT service providers, making it important for the industry to help shape future requirements.
“Certification, training, and standards are coming to this industry whether we build them or it is pushed upon us,” he said.
UK regulation signals wider change
The UK’s Cyber Security and Resilience Bill proposes bringing qualifying managed service providers (MSPs) within the scope of the Network and Information Systems Regulations 2018.
The measures would introduce cybersecurity risk-management and incident-reporting obligations for providers within scope, reflecting concerns about the potential impact of attacks on companies with access to multiple customers’ systems and data.
Asked whether governments would intervene if the MSP industry failed to establish its own standards, Wensley said the UK’s approach reflected a wider international trend.
“We do believe it will be, and what you’re doing here in the UK is an early indicator of it,” he said. “We want to be a resource to the governments who are looking to put in standards, rather than having the governments decide what standards we should abide by.”
If you liked this content…
 New Cyber Bill Aims to Keep ‘The Lights On and the Taps Running’
 UK tightens requirements for IT suppliers with new cybersecurity bill
 Cyber Security & Resilience Bill risks becoming ‘paper tiger’ without cyber skills reform, report warns
 Turning policy into practice: Implementing the UK Cyber Action Plan
 Cybersecurity and digital identity in 2026: Designing trust for a world built on deception
Wensley said similar developments were taking place in Canada, arguing that the industry needed to take a proactive role rather than wait for governments to determine its obligations.
Developing a common framework
GTIA is working with Texas A&M University through the Consortium for Responsible IT Services to develop standards for the IT services industry.
Wensley said the initiative addressed a longstanding problem: unlike many established professions, IT service providers have no universally recognised standards defining the capabilities and practices expected of them.
“Anybody could hang out a shingle and call themselves an MSP, and that holds true today,” he said.
The lack of consistent standards has become increasingly difficult to justify, he added, given MSPs’ access to customers’ intellectual property, systems and sensitive information.
The proposed framework is expected to cover technical requirements, operational competence and governance, although the precise standards have yet to be determined. Wensley revealed that GTIA members and industry specialists would lead the work, with proposals subsequently subject to wider review.
“Our members will decide on that. The experts in our membership will be the ones at the forefront of it, and then it’ll be taken out to our global community and looked at and peer reviewed and then put into practice.”
The process is expected to take two to three years, although initial recommendations could emerge before the full framework is completed.